Clear controls. Clear responsibility.
Security depends on technology, configuration and daily operations. This page states what applies to the production LevelSync service — as facts you can question, not badges. We avoid claims we cannot support.
Security controls
Identity and authentication
Two-factor authentication, password policies, lockout thresholds and session controls. Directory integration via Active Directory / Microsoft Entra ID.
Authorisation and sharing
Per-user and per-group permissions. External sharing through controlled links with passwords, expiry dates and download history.
Encryption
Data is encrypted in transit (TLS) and at rest. Further technical details about encryption and key arrangements are available from POISE as part of the security review process.
Logging and monitoring
Audit logs record logins, file actions and link activity with timestamps and user details, and can be exported for compliance reporting.
File recovery and continuity
File versioning and deleted-file recovery are available within the tenant’s configured history and retention settings. Separate infrastructure backups are maintained for disaster recovery. Restoration of individual files, folders or customer tenants from infrastructure backups is not guaranteed.
Infrastructure and operations
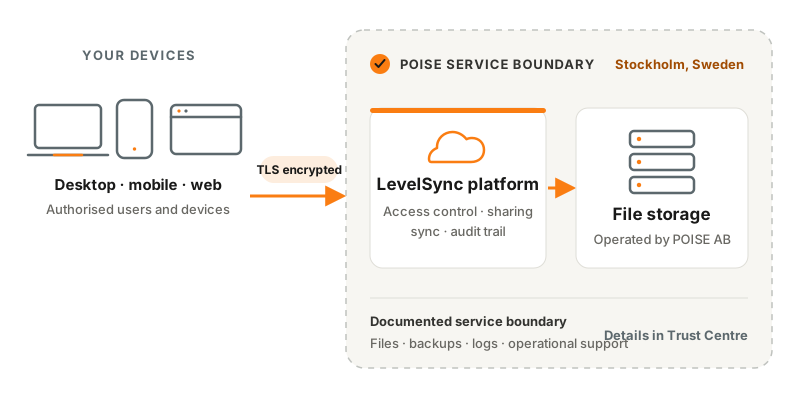
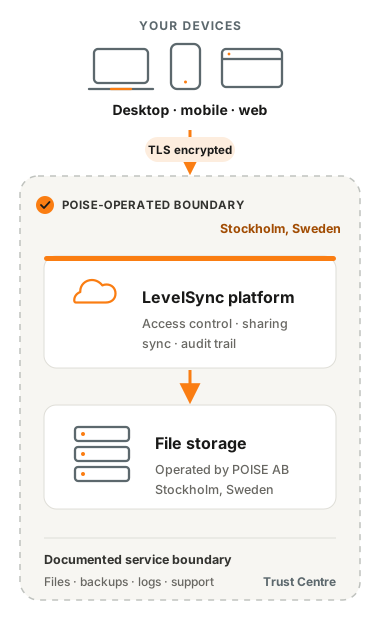
POISE AB operates the customer-facing service and infrastructure in Stockholm, applies platform updates, and provides support during Swedish business hours.
Know where the service runs
We do not hide the platform or the processing chain. LevelSync uses platform technology from RushFiles, while POISE operates the customer-facing service and infrastructure. Some operational internals — exact backup routines, monitoring details — are deliberately not published for security reasons; we walk customers through them directly during the sales and security-review process.
| Legal operator | POISE AB, Brunnsgatan 9, 172 68 Sundbyberg, Sweden — VAT SE556773092301 |
|---|---|
| Primary service location | Data center in Stockholm, Sweden |
| Platform technology | RushFiles A/S (Denmark) |
| Customer file storage | POISE-operated infrastructure at Bahnhof, Stockholm |
| Off-site backup | Encrypted infrastructure backups stored within the EU (Netherlands). Intended for disaster recovery, not for individual file restore. |
| Version history & restore | Available as a per-tenant setting — customers restore earlier file versions themselves within the configured retention. Restoration of individual files, folders or tenants from infrastructure backups is not guaranteed. |
| Monitoring & email infrastructure | EU-based, POISE-controlled — further detail available to customers on request |
| Support | POISE AB, Sweden — Swedish business hours |
| Microsoft 365 co-editing | Optional. When used, the document is processed by Microsoft's online service for the editing session. |
| Mobile push notifications | Delivered via Apple and Google notification services, as for all mobile apps |
Data export and switching
During the subscription, customers can download stored files through the supported web and client functions. Ordinary files are retrieved in their original formats; folders can be downloaded with the folder hierarchy preserved through the desktop client. For larger transfers, the desktop client is recommended.
For a move to another cloud service or to customer-operated infrastructure, customers may request an orderly transfer of exportable data and digital assets. POISE provides assistance under the LevelSync General Terms and the EU Data Act (Regulation (EU) 2023/2854) where it applies. A data transfer does not guarantee equivalent operation of platform-specific permissions, sharing links or collaboration features in the destination system.
Export register
| Files | Download through the web interface or the desktop and mobile clients, in the original file formats. Requires an authorised sign-in. |
|---|---|
| Folders and folder structure | Folder download or synchronisation through the desktop client; folder names and hierarchy are preserved. Verify that the complete selected dataset has been downloaded before the retrieval period ends. |
| Earlier file versions | Earlier versions available within the configured retention can be restored in the service and then downloaded as files. Export beyond this is handled through the documented export procedure. |
| Users, groups, permissions and sharing settings | Provided through the documented export procedure; scope and format are confirmed in writing for each request. |
| Activity and audit logs | Audit information can be exported from the administration interface. For a switching export, fields, format and retention are confirmed in the documented export procedure. |
| Formats and standards | Files are delivered in their original formats. No additional interoperability standard is applied to the other categories. |
How switching works
- Request a switch or an export by email to info@poise.se from your registered contact. Notice period: at most two months.
- Transition: completed within 30 calendar days of the end of the notice period, unless POISE notifies within 14 working days that this is technically unfeasible and proposes an alternative period of at most seven months.
- Retrieval: at least 30 calendar days after the transition to download remaining data. The transitional period can be extended once at the customer’s request.
- Switching charges: none from 12 January 2027; before that date, at most POISE’s directly incurred costs, disclosed in advance.
- After the retrieval period, customer data is erased in accordance with the General Terms and the Data Processing Agreement.
Infrastructure jurisdiction and international governmental access
LevelSync is supplied by POISE AB in Sweden. Primary customer-file infrastructure is located in Sweden and is subject to Swedish and applicable EU law. Encrypted off-site infrastructure backups are stored in the Netherlands and are subject to Dutch and applicable EU law.
POISE applies technical, organisational and contractual measures to protect data against unauthorised access and disclosure. Requests for international governmental access to non-personal data are assessed under applicable law. POISE will restrict or challenge disclosures that would conflict with EU or applicable national law to the extent legally available.
Information on personal-data processing and sub-processors is supplied to contracting customers through the Data Processing Agreement. Sensitive security configurations and internal system architecture are not disclosed publicly.
Suppliers and service components
Roles of the suppliers involved in delivering the service. Sub-processors that process customer personal data under the GDPR are listed in Annex 3 of the Data Processing Agreement, which is supplied to contracting customers.
| RushFiles A/S | Platform software supplier (Denmark, EU). Operational access arrangements are described to customers on request. |
|---|---|
| Bahnhof | Data centre colocation for POISE-operated infrastructure, Stockholm, Sweden |
| Off-site backup storage | Encrypted infrastructure backups within the EU (Netherlands); the provider is identified to contracting customers in DPA Annex 3 |
| Email delivery | POISE-operated mail server (EU) |
Contract documents
The LevelSync General Terms and Conditions apply to all customers. The Data Processing Agreement (DPA), including its sub-processor annex, is supplied to contracting customers together with the order confirmation and accepted with the order.
- LevelSync General Terms and Conditions – version 1.0 (19 October 2026), PDF · Swedish version
- LevelSync Data Processing Agreement – version 1.0 (19 October 2026): supplied to contracting customers with the order confirmation
Legitimate LevelSync domains
To protect you from phishing, these are the only domains we operate for this service:
| levelsync.com | This website — product information and contact |
|---|---|
| filesync.se | The official sign-in for the LevelSync service |
We will never ask for your password by e-mail or phone. If you receive a suspicious message that appears to come from LevelSync or POISE, forward it to us via the address below.
Report a security issue
Found a vulnerability on this website or in the service? Email us directly at security@levelsync.com — no form, no registration. A machine-readable disclosure contact is published at /.well-known/security.txt (RFC 9116). Security reports are read with priority during Swedish business hours.
We appreciate responsible disclosure and will acknowledge legitimate reports. Please do not test against production systems containing customer data.
Questions about your requirements?
Data location, integrations, onboarding — ask us directly.